TL;DR: Comp AI (trycomp.ai) is an open-source compliance platform: anyone can read its code on GitHub, and AI agents collect audit proof from 580+ integrations. It does not issue the SOC 2 report, because an independent auditor does. Price is a quote after a 20-minute call, with a money-back guarantee. It suits startups. Prices are as of 20 October 2026.
How Comp AI reads on five points
| Quick facts | Comp AI |
|---|---|
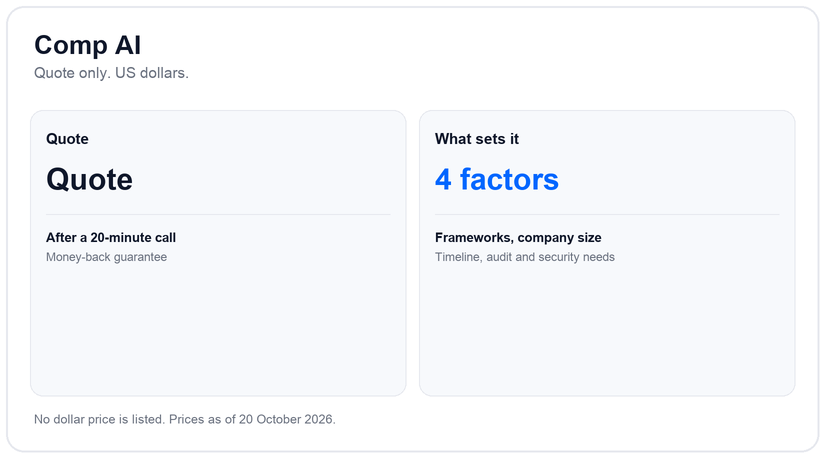
| Price | Quote after a 20-minute call. A money-back guarantee comes with it |
| What sets the price | Frameworks, company size, timeline, and audit and security needs |
| Frameworks | SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, SOC 1, NIST, ISO 42001, ISO 9001, CCPA, FedRAMP and more |
| Integrations | 580+ |
| Auditor | Any accredited auditor. An independent auditor produces the report |
| Open source | Yes. The code, the integrations and the device agent are on GitHub |
| Fits | Founders who want open code and a choice of auditor |
Compliance automation software does the repeat work around a security audit. A framework is a set of security rules, such as SOC 2 or ISO 27001. An auditor is an outside firm that checks your security. Evidence is the proof an auditor wants, such as a record that every laptop is encrypted. Comp AI uses AI agents to collect that evidence, write your policies and watch your systems. Open source means the code is public, so anyone can read it.
Key features of Comp AI
- Open source: the platform's code, its integrations and its device agent are on GitHub, so you can read how they work.
- 580+ integrations: AI agents connect to your cloud host, HR system, payment tools and engineering tools, then collect evidence such as screenshots and documents.
- AI-written policies: the agents write policies from how your business runs, and you review and approve each one before it goes live.
- Device agent: an open-source program on each work laptop that checks disk encryption, firewall, screen lock, password length and antivirus.
- AI penetration testing: agents probe your code and APIs. A penetration test is a security test where someone tries to break into your systems.
- Trust center: a live web page where you share security documents with buyers. Controls that fail are removed from it automatically.
- Vendor and risk monitoring: risk scores, vendor management and alerts before an issue becomes an audit finding.
- Slack support: a dedicated Slack channel with in-house experts, and email support.
Who Comp AI fits
- If you want to read the code of the tool that watches your systems, Comp AI is open source.
- If you already work with an audit firm, Comp AI works with any accredited auditor.
- If you want a Slack channel with experts instead of a ticket queue, each customer gets a dedicated Slack channel.
- If you want to see a price before you talk to anyone, Secureframe starts at $7,500 a year and Strike Graph's Scale plan at $21,500 a year (as of 20 October 2026). Comp AI gives a quote on a 20-minute call.
- If you want a guarantee, Comp AI puts a money-back guarantee next to its quote. Ask what it covers.
Comp AI pricing
Comp AI is quote only. There is no dollar price. You fill in a short form, pick a time and get your number on a 20-minute call. Prices are in US dollars as of 20 October 2026.
| Item | What to know |
|---|---|
| Price | Quote after a 20-minute call. There is no dollar price |
| What sets the price | The frameworks in scope, company size, timeline, and audit and security needs |
| Several frameworks | The quote covers the frameworks you scope. Controls map across frameworks, so a second framework costs less than starting from scratch |
| Audit, penetration testing, trust center | Whether you need them changes what is included, so ask what your quote covers |
| Guarantee | A money-back guarantee comes with the quote |
An independent auditor conducts the audit and produces the report, so the audit fee is set by the auditor. Ask whether your quote includes the audit or only the platform.
Timelines vary by framework and company complexity. Ask for a start date and a target date in writing.
Who signs your SOC 2 report if you use Comp AI?
An independent auditor does. Comp AI does not generate the report. It prepares you by organizing evidence, controls and policies, and then the auditor conducts the audit and produces the report. Comp AI works with any accredited auditor of your choice.
What should you ask before you buy Comp AI?
- What does the quote include: the platform only, or also the audit, penetration testing and a trust center?
- Which accredited auditor will you use, and what is its fee?
- What does the second framework cost?
- What does the money-back guarantee cover, and for how long?
- What is the price in year two?
Comp AI terms in plain words
- Open source: software whose code is public, so anyone can read it.
- SOC 2 report: a report from an independent audit firm on how your company protects customer data.
- ISO 27001: an international standard for managing information security, certified by an independent body.
- Device agent: a small program on each work laptop that checks its security settings.
- Penetration test: a security test where someone tries to break into your systems.
- Trust center: a web page where you share security documents with buyers.
Pros and good to know
Pros
- Open-source code, integrations and device agent
- 580+ integrations
- Works with any accredited auditor
- A money-back guarantee with the quote
- A dedicated Slack channel with in-house experts
Good to know
- An independent auditor produces the report, so ask whether the audit fee sits in your quote.
- The price comes only after a 20-minute call.
Best for your situation
Guides & comparisons
Frequently Asked Questions
How much does Comp AI cost?
Comp AI is quote only. You fill in a short form, pick a time and get your price on a 20-minute call. Four things set the price: the frameworks, your company size, your timeline, and your audit and security needs. A money-back guarantee comes with it. Prices as of 20 October 2026.
Is Comp AI open source?
Yes. You can read the platform's code on GitHub, and the integrations and the device agent are open source too.
Can I bring my own auditor to Comp AI?
Yes. Comp AI works with any accredited auditor of your choice. An independent auditor conducts the audit and produces the report.
Does Comp AI generate the SOC 2 report?
No. The auditor generates and uploads the audit report. Comp AI prepares you by organizing evidence, controls and policies.
Which frameworks does Comp AI cover?
SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, SOC 1, NIST, ISO 42001, ISO 9001, CCPA, FedRAMP and more. A quote covers the frameworks you scope.
How long does it take to get audit-ready with Comp AI?
It varies by framework and company complexity. Ask for a start date and a target date in writing, and ask your audit firm when it can begin.
Does Comp AI make you SOC 2 compliant?
No software does. Comp AI collects evidence and tracks your rules, and an independent auditor tests your controls and issues the report.
What are alternatives to Comp AI?
Secureframe starts at $7,500 a year and Strike Graph's Scale plan at $21,500 a year (as of 20 October 2026). Vanta, Drata, Sprinto and Oneleet give a price after a demo or a call.
Bottom line
Comp AI fits a founder who wants open code, 580+ integrations and the freedom to keep any accredited auditor, and who is fine getting a price on a call. Before you buy, ask what the quote includes beyond the platform, ask what the money-back guarantee covers and ask for the audit fee separately. Prices are as of 20 October 2026.
Add us as a preferred source on Google, and our reviews and picks show up in your Top Stories and AI Overviews.